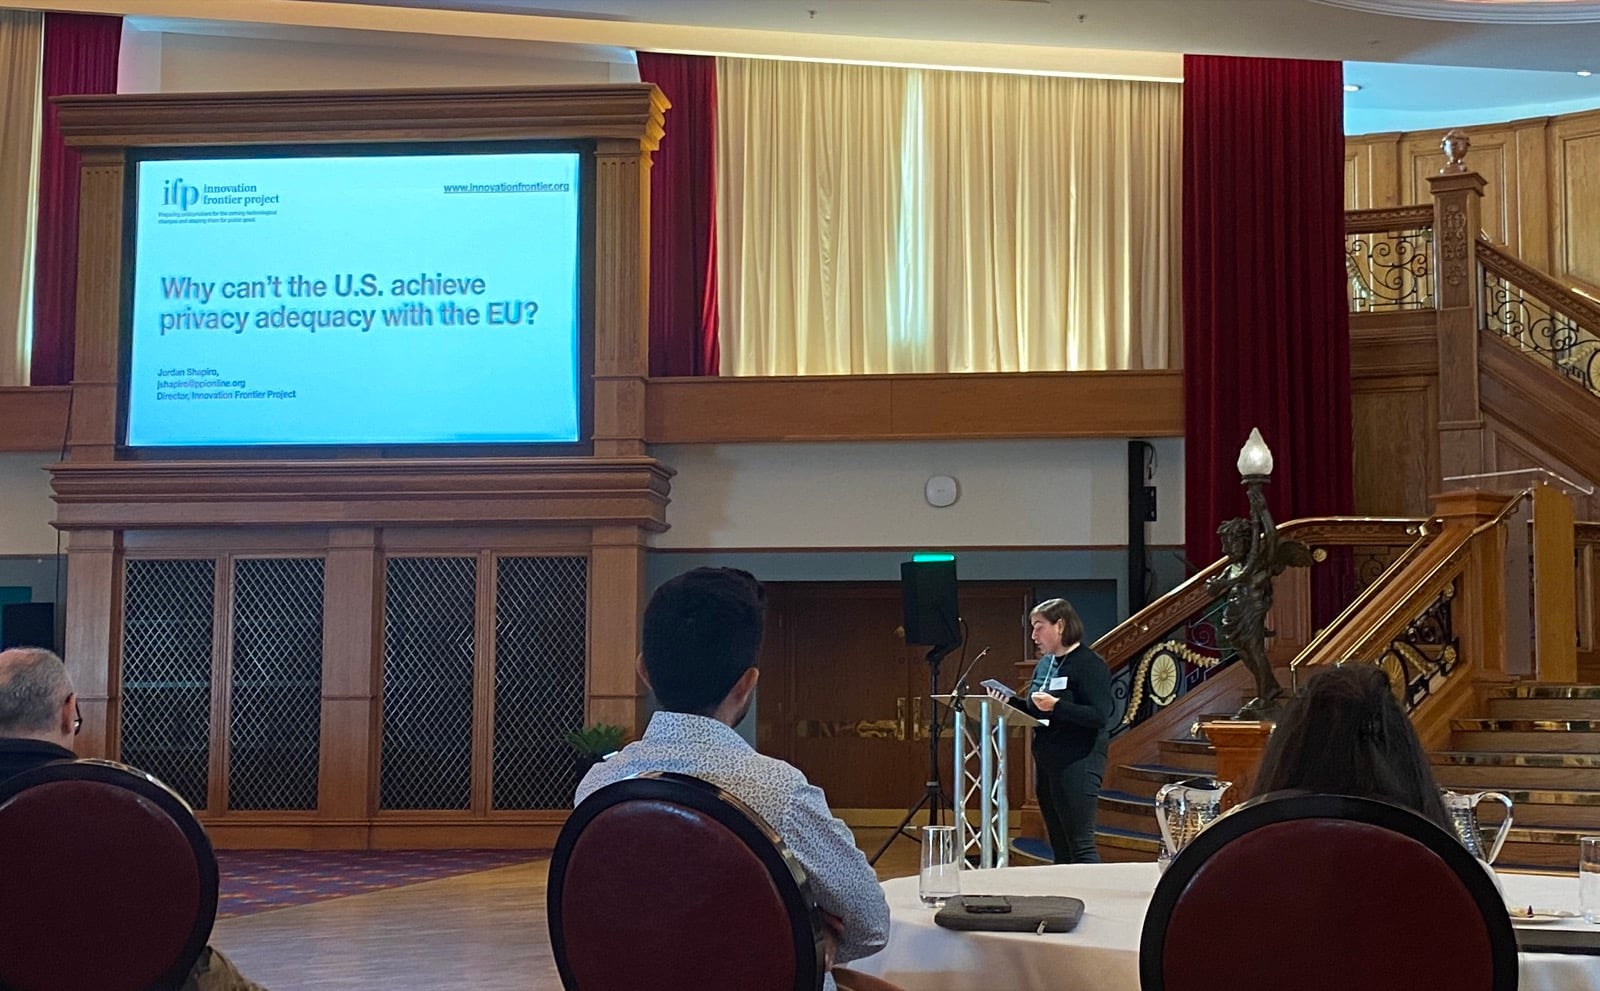
Why can't the U.S. achieve privacy adequacy with the EU?
Lightning talk · SPRITE+ Conference, Titanic Centre, Belfast · Wednesday 28 June 2023
Jordan Shapiro, Director, Innovation Frontier Project
Listed in the programme as “Why Can't the United States Gain Privacy Adequacy with the EU?”
Speaker for the Sprite+ Hub for Trust, Identity, Privacy, and Security.
The state of U.S. data privacy
After 10 years of trying, why can’t the U.S. achieve privacy adequacy with the EU? The disagreements in the technology landscape between the United States and the European Union are well documented. Though few are as thorny as the inability to form a long-lasting agreement for transatlantic data flows: privacy adequacy.
We live in a world where the internet knows no borders, where ideas flow freely across nations thanks to technology. In this interconnected digital realm, modern democracies are facing a challenge in the realm of data privacy whereby the United States and the European Union are grappling with differences in law, culture, and approach when it comes to personal data.
The fundamental, and perhaps the most obvious reason, the United States cannot achieve privacy adequacy with the EU is due to law: the absence of a comprehensive federal privacy law in America that explicitly defines the rights of citizens and the responsibilities of businesses in handling personal data. Instead, we find a patchwork of regulations at the state and sectoral levels. It’s a complex web that makes it challenging to achieve the same level of protection and harmony as our European counterparts.
The United States came close to passing a federal privacy law in late 2022 with the American Data Privacy and Protection Act (ADPPA). This bill garnered support from three out of the four most influential Congressional committees, making it a promising option for privacy advocates in Washington, D.C. However, its progress was halted due to conflicts with state regulations, particularly the California Consumer Privacy Act, ultimately preventing it from being brought to a vote on the House floor.
While the bill encompassed several principles of the GDPR, its passage alone might not have guaranteed privacy adequacy due to the U.S. differences in culture and approach to data privacy.
Long before the implementation of the General Data Protection Regulation (GDPR), the EU emphasized the importance of stringent privacy and security measures when transferring data of its citizens beyond its borders. Current challenges on transatlantic data transfers are just the newest iteration of these differing cultural values.
In the United States, however, a different narrative unfolds. The United States’ definition of what is adequate data protection is simply different than what is considered adequate from an EU standpoint. The US holds that not all personal data requires the highest levels of data protection. More specifically, the economic and innovative utility of some types of personal data, such as that used to train artificial intelligence or for business and government intelligence, outweighs the need to protect all personal data.
Instead, the United States separates privacy needs by sector. This strategy implements privacy safeguards in place for critical areas such as health, finance, and personal data stored by the government.
These legal and cultural differences in the public-private space give rise to my final, and one of the most fundamental, reasons that the United States cannot achieve privacy adequacy with the EU: how the government perceives surveillance versus personal privacy.
The E.U. is particularly concerned about the surveillance practices by the US government and intelligence agencies. Revelations by Edward Snowden in 2013 exposed the extent of US surveillance programs, such as PRISM, which involved the collection of personal data from non-US citizens even without suspicion of wrongdoing. These surveillance practices, coupled with the lack of redress for Europeans to raise privacy violations in the United States, are inconsistent with EU data protection principles.
I’m sure familiar to people in this room, the EU requires a legal remedy in the United States for Europeans who believe their privacy has been violated, but the U.S. legal system does not have such protections.
The efforts toward ensuring transatlantic data flows by diplomats on both sides of the pond belie the challenge in finding common ground. These factors: legal, cultural, and privacy approach have all contributed to the disagreement.
The challenge we face is creating a harmonious technological future. Not a small challenge. The benefits of technology are vast and ought to be available to all. This future is at risk if internet regulations in different localities are not interoperable.
The disparities in the legal technology landscape, coupled with cultural differences and varying approaches to data privacy, have created a complex web of challenges. My work seeks to find an equilibrium where privacy rights are upheld, innovation flourishes, and the immense potential of data is unlocked. Only by bridging these gaps in a transatlantic way can we pave the way for a future where privacy and progress coexist in harmony.